

Welcome to the weekly highlights and analysis of the blueteamsec (and my wider reading). Not everything makes it in, but the best bits do.
Operationally this week React2Shell exploitation continues as does a plethora of other at scale exploitation examples (see below). It is safe to say this is a now an trend by a range of threat actors - namely when a vulnerability becomes known it is globally exploited and then the victims triaged..
In the high-level this week:
Speech by Blaise Metreweli, Chief of SIS, 15 December 2025 - Secret Intelligence Service, Foreign, Commonwealth & Development Office and Blaise Metreweli publish - “Alongside the grinding war, Russia is testing us in the grey zone with tactics that are just below the threshold of war. It’s important to understand their attempts to bully, fearmonger and manipulate, because it affects us all.
I am talking about:
Cyberattacks on critical infrastructure.
Drones buzzing airports and bases.
Aggressive activity in our seas, above and below the waves.
State-sponsored arson and sabotage.
Propaganda and influence operations that crack open and exploit fractures within societies.”
DSIT cyber security newsletter - December 2025 - Department for Science, Innovation & Technology publish - “While there have been many successes since our last update, probably the most anticipated has been the introduction of the Cyber Security and Resilience Bill to Parliament in November. This was preceded by months (and years!) of hard work by the Bill team, policy officials across DSIT and government, and a wide range of industry colleagues. The Bill is a key milestone in our goal to make the UK economy more secure, resilient and prosperous.”
The third UK-EU Cyber Dialogue took place in Brussels - Foreign, Commonwealth & Development Office and Department for Science, Innovation and Technology announce - “The agenda included exchanges of views on our respective approaches to cyber legislation to ensure high levels of cyber security while minimising compliance burdens on industry; deterrence strategies against cyber threats; countering cybercrime; cyber capacity building; incident response; and working with the multi-stakeholder community to uphold a free, open, secure and peaceful cyberspace.”
Lieutenant General Sir Rob Magowan appointed new Commander of Cyber & Specialist Operations Command - Ministry of Defence and The Rt Hon John Healey MP announce - “General Rob will be responsible for overseeing Defence’s cyber and specialist forces – including cyber experts, deployments and operations through the Permanent Joint Headquarters, medical support, intelligence, educators, and UK Defence attachés.”
Mapping IoT security publications on Enterprise IoT security - Department for Science, Innovation and Technology publish - “In summer 2025 the government ran a call for views on a proposed Code of Practice for Enterprise Connected Device Security. This research reports maps various IoT security publications to the proposed code of practice.”
Evaluation of the UKC3 programme 2024-2025 - Department for Science, Innovation and Technology publish - “Only 10% of cluster leaders responding to the survey reported they have secured long-term funding in the past 12 months. This suggests that some clusters may reduce or cease activities into the next financial year, or move to a more voluntary model, subject to wider funding availability.”
UK security export statistics 2024 - Department for Business & Trade publish - cyber was £8.6billion
Inquiry ongoing after UK government hacked, says minister - BBC reports - Speaking earlier on BBC Breakfast, Sir Chris said the security gap was “closed pretty quickly” and “we think that it is a fairly low-risk that individuals will have been compromised or affected”.
Pax Silica Summit - US Department of State summarise - “Pax Silica is a U.S.-led strategic initiative to build a secure, prosperous, and innovation driven silicon supply chain—from critical minerals and energy inputs to advanced manufacturing, semiconductors, AI infrastructure, and logistics.”
Russia is responsible for destructive and disruptive cyberattacks against Denmark - Danish Defence Intelligence Service attribute - “The Danish Defence Intelligence Service (DDIS) assesses that Russia was behind a destructive cyber-attack on a Danish water utility in 2024 and a series of DDoS attacks on Danish websites in the run-up to the 2025 municipal and regional council elections”
MIVD Annual Plan 2026 - MIVD publishes - “In 2026, the MIVD (Military Intelligence and Security Service) will explicitly focus on disrupting and exposing cyber operations by both state and non-state actors. A key objective of the MIVD’s cyber investigations is also to inform (international) victims and provide resilience-enhancing measures.”
Public enquiry concerning the new draft standard prEN 40000-1-3 ‘Vulnerability Handling’, in support of the Cyber Resilience Act - Agoria report - “More specifically, this standard aims to address Part II of Annex I of the CRA, which contains 8 requirements relating to vulnerability handling. Given that product-specific (or “vertical”) standards will only cover aspects related to Part I of Annex I of the CRA, this horizontal standard is very important as it is the only CRA standard that will cover the vulnerability handling aspects.”
The Cyber Defense Review - US Army publishes - Special Issue on Cyber Resilience and Power Projection
Retour d’expérience (RETEX) de l’exercice REMPAR25 - ANSSI publish - report is in French, Google translate works - “Throughout the day, nearly 5,680 professionals participated in the exercise, 50% of whom worked in fields other than digital technology or cybersecurity. Representing 1,263 public and private organizations across 13 regions and 9 overseas territories, they were asked to respond to the impacts of a systemic cyber crisis, simulating a massive disruption of essential digital services and resulting in impacts across multiple sectors and for numerous stakeholders.”
U.S. Cyber Command’s “Operation Hunt Forward” (2018-2025) - National Institute for Defence Studies, Japan publishes - report is in Japanese - “First, based on the deployment of HFO before Russia’s full-scale invasion of Ukraine, there are strong voices both domestically and internationally that view HFO as the most successful example of cyber defense cooperation between allied and like-minded nations in recent years, and that hopes are strong for exporting Ukraine’s successful model and replicating it in Northeast Asian crises, including those in the Taiwan Strait”
Digital Transformations of Ukraine’s Cybersecurity System in Wartime - Monograph publishes - “Cybersecurity, once perceived as a technical or sector-specific concern, has emerged as a strategic foundation for national security and sovereignty. Wartime realities emphasized that without safeguarded digital infrastructure: communications networks, public registries, financial systems, energy grids, and civilian services, a state’s ability to govern, coordinate defense, and maintain societal stability becomes severely compromised.”
Preparing for Migration to Post Quantum Cryptography - US Department of War publishes - “To assess risk and track PQC migration, it is imperative to identify and inventory any type of cryptography used in all DoW information systems including, but not limited to, national security systems (NSS), non-NSS, business systems, weapons systems, cloud computing capabilities, mobile devices, physical access control systems, internet of things, unmanned systems, and operational technology, regardless of classification, location, connection, type, purpose, or use.”
Cybersecurity Performance Goals 2.0 for Critical Infrastructure - CISA releases - “CPG 2.0 includes a new component focused on the essential role of governance in managing cybersecurity. It emphasizes accountability, risk management, and strategic integration of cybersecurity into day-to-day operations, reinforcing the principle that effective governance is the cornerstone of a resilient cyber posture.”
Peters & Cornyn Reintroduce Legislation to Protect Commercial Satellites from Cybersecurity Threats - U.S. Senators Gary Peters (D-MI), Ranking Member of the Homeland Security and Governmental Affairs Committee, and John Cornyn (R-TX) reintroduce - “the bipartisan Satellite Cybersecurity Act to help commercial satellite owners and operators defend against growing cybersecurity threats.”
‘The hunt has begun’: Iran-linked hackers put bounties for info on Israeli air defense developers - The Jerusalem Post reports - “The Handala hacker group on Saturday offered a $30,000 bounty on information on Israeli engineers and technicians, listing their photos, names, credentials, email addresses, locations, and phone numbers.”
Doxers Posing as Cops Are Tricking Big Tech Firms Into Sharing People’s Private Data - WIRED reports - “This took all of 20 minutes,” Exempt, a member of the group that carried out the ploy, told WIRED. He claims that his group has been successful in extracting similar information from virtually every major US tech company, including Apple and Amazon, as well as more fringe platforms like video-sharing site Rumble, which is popular with far-right influencers.”
European Software and Cyber Dependencies - European Parliament publishes - “Europe’s digital ecosystem remains heavily dependent on non-EU software and cloud providers. This study maps these dependencies, as well the geopolitical and economic risks they raise. “
Reporting on/from China
The Many Arms of the MSS: Why Provincial Bureaus Matter in China’s Cyber Operations - Natto Thoughts and Eugenio Benincasa - “The MSS is not a monolith: it is highly provincialized, with bureaus that cultivate their own bureaucratic interests, talent pipelines, and trusted ecosystems of companies and individual professionals and researchers.”
Krishnamoorthi Introduces SAFE LiDAR Act to Phase-Out Chinese-Made LiDAR from the United States - Congressman Raja Krishnamoorthi, Ranking Member of the House Select Committee on the Strategic Competition Between the United States and the Chinese Communist Party announces - “The SAFE LiDAR Act takes a proactive, commonsense step to secure our supply chains, protect advanced technologies from compromise, enhance Americans’ security, and ensure these systems are built by trusted partners. America and our allies should lead in LiDAR innovation—not cede control of this critical technology to foreign adversaries who will use their control to endanger Americans.”
U.S. Grid Exposed to Risk from PRC-Made Inverter Equipment - Strider Intelligence hyperboles - “This widespread reliance creates a strategic vulnerability: the Chinese government, through its control over PRC firms and data networks, could exploit this access to manipulate or disrupt the U.S. grid in a crisis”
How China built its ‘Manhattan Project’ to rival the West in AI chip - Reuters reports - “In a high-security Shenzhen laboratory, Chinese scientists have built what Washington has spent years trying to prevent: a prototype of a machine capable of producing the cutting-edge semiconductor chips that power artificial intelligence, smartphones and weapons central to Western military dominance, Reuters has learned.”
Meta adopts Qwen as Chinese AI becomes industry foundation - South China Morning Post reports - “According to a Bloomberg report on Wednesday, it was now Meta that is reportedly taking its cues from Alibaba, with unnamed sources claiming that the Facebook owner was now using Qwen to help train a new model code-named Avocado.”
AI
Frontier AI Trends Report: PDF - AI Security Institute publish - “In the cyber domain, Al models can now complete apprentice-level tasks 50% of the time on average, compared to just over 10% of the time in early 2024” - important points here are the level (apprentice) and likelihood of completion (1 in 2)
AI Insights: Prompt Risks - Government Digital Service publish - “All communicated data must be monitored and evaluated without exception. The responses received from our generative AI systems must be examined and sanitised before return. Our systems must have security built-in at all levels. We treat safeguarding as a principal responsibility, not as a bolt-on addition, nor as an afterthought.”
Fact Sheet: President Donald J. Trump Ensures a National Policy Framework for Artificial Intelligence - The White House (not me) announces - “The Order directs the Attorney General to establish an AI Litigation Task Force to challenge unconstitutional, preempted, or otherwise unlawful State AI laws that harm innovation.”
Cybersecurity Framework Profile for Artificial Intelligence (Cyber AI Profile): NIST Community Profile - NIST publish draft for comment - “The Cyber AI Profile addresses the following Focus Areas:
Securing AI System Components (Secure)
Conducting AI-Enabled Cyber Defense (Defend)
Thwarting AI-enabled Cyber Attacks (Thwart)”
VulnLLM-R: Specialized Reasoning LLM with Agent Scaffold for Vulnerability Detection - Many organisations collaborate and publish - “We construct an agent scaffold around our model and show that it outperforms CodeQL and AFL++ in realworld projects. Our agent further discovers a set of zero-day vulnerabilities in actively maintained repositories.”
Vulnhalla: Picking the true vulnerabilities from the CodeQL haystack - Simcha Kosman engineers - “By layering an LLM on top of CodeQL, we significantly reduce the overwhelming noise of false positives that typically buries security teams. The result is a workflow where developers and security researchers can focus only on findings that have genuine potential to be exploited.”
Llama-based source code vulnerability detection: Prompt engineering vs Fine tuning - University of Mons publishes - “We leverage the recent open-source Llama-3.1 8B, with source code samples extracted from BigVul and PrimeVul datasets. Our conclusions highlight the importance of fine-tuning to resolve the task, the performance of Double tuning, as well as the potential of Llama models for CVD.”
We're Not Ready for AI's Risks - Time Magazine op eds to level 11 - “For instance, several model developers reported over the summer that frontier AI systems had crossed new thresholds concerning biological risks. This is largely attributable to significant advances in reasoning since late 2024. A key concern is that, without adequate safeguards, these models possess the capacity to enable those without biological expertise to undertake potentially dangerous bioweapon development.”
Separating Hype from Hazard: The Truth About Autonomous AI Hacking - Heather Adkins, VP of Security Engineering, Google podcasts
Search engines in times of Artificial Intelligence - European Parliament publishes - “According to experts, users are less likely to click on links when Google's AI summary is provided. They also believe that users are now structuring search queries differently and are increasingly using natural language in voice commands.” - the value of Search Engine Optimisation for malicious purposes just went up…
Toward Quantitative Modeling of Cybersecurity Risks Due to AI Misuse - Many organisations collaborate and publish - “We aim for our quantitative risk modeling to fulfill several aims: to help cybersecurity teams prioritize mitigations, AI evaluators design benchmarks, AI developers make more informed deployment decisions, and policymakers obtain information to set risk thresholds.”
Weird Generalization and Inductive Backdoors: New Ways to Corrupt LLMs - Many organisations collaborate and publish - “We also introduce inductive backdoors, where a model learns both a backdoor trigger and its associated behavior through generalization rather than memorization. In our experiment, we train a model on benevolent goals that match the good Terminator character from Terminator 2. Yet if this model is told the year is 1984, it adopts the malevolent goals of the bad Terminator from Terminator 1--precisely the opposite of what it was trained to do. Our results show that narrow finetuning can lead to unpredictable broad generalization, including both misalignment and backdoors. Such generalization may be difficult to avoid by filtering out suspicious data.”
Memory Injection Attacks on LLM Agents via Query-Only Interaction - Michigan State University, University of Georgia and Singapore Management University publish - “In this paper, we propose a novel Memory INJection Attack, MINJA, without assuming that the attacker can directly modify the memory bank of the agent. The attacker injects malicious records into the memory bank by only interacting with the agent via queries and output observations.”
ToolShell, Patch Bypass, and the AI That Might Have Seen It Coming - Soroush Dalili and Pedram Hayati detail - “Use AI for: "Find me inputs that can lead into unhandled/undecided program states" - Fuzzing”
Task Injection – Exploiting agency of autonomous AI agents - Jun Kokatsu details - “describes what a Task Injection attack is, how this type of attack differs from Prompt Injection, and how it is particularly relevant to AI agents designed for a wide range of actions and tasks, such as computer-use agents.”
Legal Reviews of War Algorithms: From Cyber Weapons to AI Systems - Lieber Institute, West Point ponder - “There are jus ad bellum considerations as well. While Articles 2(4) and 51 of the UN Charter do not refer to specific weapons, use of autonomous capabilities embedded in cyber weapons or AI decision support systems remains subject to the rules on self-defense, necessity, and proportionality. Controversies and grey areas regarding the occurrence of “attacks”, notably in the digital sphere, could make related reviews complex or inconclusive.”
Cyber proliferation
RSF uncovers new spyware from Belarus - Reporters without Boarders uncovers - “The spyware, initially labelled “ResidentBat” when identified, targets Android smartphones and enables access to highly sensitive data. Unlike well-known spyware products used against journalists such as Pegasus, ResidentBat does not exploit digital vulnerabilities. Instead, it is installed after security forces gain physical access to a device. “
Bounty Hunting
Ministry of the Interior breach arrest - Paris Court announces - “A person was arrested on December 17, 2025, as part of an investigation opened by the cybercrime unit of the Paris prosecutor’s office, on charges including attacking an automated personal data processing system implemented by the State as part of an organized group, following the cyberattack against the Ministry of the Interior.”
Second Seafarer Arrested in Ferry Malware Case - Maritime Executive reports - “Italian police have arrested a second Latvian suspect in connection with an attempted malware attack aboard a Mediterranean ferry, expanding the international scope of the investigation.”
Google sues alleged Chinese scam group behind massive U.S. text message phishing ring - NBC reports - “The lawsuit is designed to give Google legal standing so U.S. courts will allow it to seize websites the group uses, hampering their operations, a spokesperson said.”
2025 Crypto Theft Reaches $3.4 Billion - Chainalysis analyses - “North Korean hackers stole $2.02 billion in cryptocurrency in 2025, a 51% year-over-year increase, pushing their all-time total to $6.75 billion.”
Market Incentives
Supplementing Regulation (EU) 2024/2847 of the European Parliament and of the Council by specifying the terms and conditions for applying the cybersecurity-related grounds in relation to delaying the dissemination of notifications - European Union publishes - “This Delegated Act is therefore intended to supplement the Cyber Resilience Act by specifying the terms and conditions for applying the cybersecurity-related grounds to delay the dissemination of notifications. It does so by identifying three types of reason for which the CSIRT initially receiving the notification may decide that it is necessary to delay further dissemination to other CSIRTs. Such a decision to delay may be taken in three circumstances:
in the light of an evaluation of the nature of the notified information;
if the CSIRT receiving the notification is unable to ensure the confidentiality of such information;
if the single reporting platform has been compromised or is temporarily not operational.”
Science minister vows punitive fines against companies with repeated security breaches - The Korea Times reports - “In detail, the ministry said it will seek to codify the responsibility of chief executive officers under relevant laws and strengthen the authority of chief security officers.”
Meta tolerates rampant ad fraud from China to safeguard billions in revenue - Reuters reports - “Meta calculated that about 19% of that money – more than $3 billion – was coming from ads for scams, illegal gambling, pornography and other banned content, according to internal Meta documents reviewed by Reuters.”
DXS International plc (AQSE:DXSP) Notice of Cyber Security Incident - DXS International plc details - “The Company has notified the relevant regulators, authorities, and law enforcement agencies, including the Information Commissioner’s Office, and various NHS bodies and is fully cooperating with their investigations.. The Company does not currently anticipate that this incident will have a material adverse impact on its financial position or on the market forecasts for its financials for FY 30 April 2026.”
8 Million Users’ AI Conversations Sold for Profit by “Privacy” Extensions - Koi allege - “To be fair, Urban VPN does disclose some of this-if you know where to look. …
Before version 5.5.0: No AI harvesting functionality
July 9, 2025: Version 5.5.0 released with AI harvesting enabled by default
July 2025 - Present: All user conversations with targeted AI platforms captured and exfiltrated”
Reflections this week are simply a big thank you for all the feedback I receive on this weekly note…
I bump into a lot of you at conferences, in meetings and other events across the globe and as I say to each of you - this is a labour of love and I am glad you enjoy it.
So with that have a very Merry Christmas and to all the cyber defenders working the holidays your commitment is so deeply appreciated!
Not getting this via email? Subscribe:
Think someone else would benefit? Share:
All attribution is by others and not the UK Government unless specifically stated as such, please see the legal text at the end.
Have a lovely Saturday…
Ollie
Cyber threat intelligence
Who is doing what to whom and how allegedly.
Reporting on Russia
Russian APT actor phishes the Baltics and the Balkans
StrikeReady Labs detail this alleged Russian operation which is insightful in so much as it highlights victimology and methods.
On December 5th, a Russian APT targeted Transnistria’s governing body with a credential phishing email attachment, spoofing the Pridnestrovian Moldavian Republic.
https://strikeready.com/blog/russian-apt-actor-phishes-the-baltics-and-the-balkans/
BlueDelta’s Persistent Campaign Against UKR.NET
Insikt Group® detail an alleged Russian operation which shows why moving to phishing resistant multi-factor authentication should be at the top of every organisations Christmas list be it for your employees or users.
[We] identified a sustained credential-harvesting campaign targeting users of UKR.NET, a widely used Ukrainian webmail and news service. The activity is attributed to the Russian state-sponsored threat group BlueDelta (also known as APT28, Fancy Bear, and Forest Blizzard)
https://www.recordedfuture.com/research/bluedeltas-persistent-campaign-against-ukrnet
Amazon Threat Intelligence identifies Russian cyber threat group targeting Western critical infrastructure
CJ Moses summarises alleged Russian operations and the initial access mechanisms. The 2025 edge device compromises underlines the value of all vendors implement NCSC’s Guidance on digital forensics and protective monitoring specifications for producers of network devices and appliances
Amazon Threat Intelligence observed sustained targeting of global infrastructure between 2021-2025, with particular focus on the energy sector. The campaign demonstrates a clear evolution in tactics.
Timeline:
2021-2022: WatchGuard exploitation (CVE-2022-26318) detected by Amazon MadPot; misconfigured device targeting observed
2022-2023: Confluence vulnerability exploitation (CVE-2021-26084, CVE-2023-22518); continued misconfigured device targeting
2024: Veeam exploitation (CVE-2023-27532); continued misconfigured device targeting
2025: Sustained targeting of misconfigured customer network edge device targeting; decline in N-day/zero-day exploitation activity
Primary targets:
Energy sector organizations across Western nations
Critical infrastructure providers in North America and Europe
Organizations with cloud-hosted network infrastructure
Commonly targeted resources:
Enterprise routers and routing infrastructure
VPN concentrators and remote access gateways
Network management appliances
Collaboration and wiki platforms
Cloud-based project management systems
Reporting on China
LongNosedGoblin tries to sniff out governmental affairs in Southeast Asia and Japan
Anton Cherepanov and Peter Strýček detail an alleged Chinese group who has a regional focus. Insightful for the length of time they have been active as well some of their lateral movement tradecraft.
LongNosedGoblin is a newly discovered China-aligned APT group targeting governmental entities in Southeast Asia and Japan, with the goal of cyberespionage.
The group has been active since at least September 2023.
LongNosedGoblin uses Group Policy to deploy malware across the compromised network, and cloud services (e.g., Microsoft OneDrive and Google Drive) as command and control (C&C) servers.
One of the group’s tools, NosyHistorian, is used to gather browser history and decide where to deploy further malware, such as the NosyDoor backdoor.
NosyDoor is most likely being shared by multiple China-aligned threat actors.
UAT-9686 actively targets Cisco Secure Email Gateway and Secure Email and Web Manager
Cisco Talos detail the exploitation of these devices by as as-yet unknown by allegedly Chinese threat actor.
Cisco Talos recently discovered a campaign targeting Cisco AsyncOS Software for Cisco Secure Email Gateway, formerly known as Cisco Email Security Appliance (ESA), and Cisco Secure Email and Web Manager, formerly known as Cisco Content Security Management Appliance (SMA).
We assess with moderate confidence that the adversary, who we are tracking as UAT-9686, is a Chinese-nexus advanced persistent threat (APT) actor whose tool use and infrastructure are consistent with other Chinese threat groups.
As part of this activity, UAT-9686 deploys a custom persistence mechanism we track as “AquaShell” accompanied by additional tooling meant for reverse tunneling and purging logs.
Our analysis indicates that appliances with non-standard configurations, as described in Cisco’s advisory, are what we have observed as being compromised by the attack.
https://blog.talosintelligence.com/uat-9686/
Inside Ink Dragon: Revealing the Relay Network and Inner Workings of a Stealthy Offensive Operation
Check Point Research detail an alleged Chinese operation which uses misconfigured or otherwise insecure Microsoft IIS servers as C2 nodes. As states look to avoid attribution one can expect C2 infrastructure to be built from everything and anything.
In recent months, Check Point Research has identified a new wave of attacks attributed to the Chinese threat actor Ink Dragon. Ink Dragon overlaps with threat clusters publicly reported as Earth Alux, Jewelbug, REF7707, CL-STA-0049, among others.
Ink Dragon has expanded its operational focus to new regions – In the last few months, the threat actor’s activities show increased focus on government targets in Europe in addition to continued activities in Southeast Asia and South America.
Ink Dragon builds a victim-based relay network – Ink Dragon leverages a custom ShadowPad IIS Listener module to turn compromised servers into active nodes within a distributed mesh, allowing each victim to forward commands and traffic, effectively transforming targets into part of their C2 infrastructure.
Ink Dragon continues to exploit long-known IIS misconfigurations for initial access – Despite years of public reporting and awareness within the security community, Ink Dragon still relies on predictable or mismanaged ASP.NET machineKey values to perform ViewState deserialization attacks against vulnerable IIS and SharePoint servers.
https://research.checkpoint.com/2025/ink-dragons-relay-network-and-offensive-operation/
Reporting on North Korea
Technical Analysis of APT-C-26 (Lazarus) Group’s Deployment of the Blank Grabber Trojan Using a WinRAR Vulnerability
Chinese reporting on an alleged North Korean operation to go after credentials and wallets using an n-day vulnerability via e-mail.
[We] captured a new sample from the Lazarus group that uses the WinRAR vulnerability CVE-2025-8088 for poisoning attacks. Attackers disguise RAR files containing malicious scripts as legitimate toolkits to lure users into downloading them. Once the victim unzips the file, the malicious script is released, subsequently downloading a Blank Grabber information-stealing Trojan. This Trojan primarily targets passwords, cookies, and autofill data in Chromium-based browsers, steals complete Discord and Telegram sessions, and steals seed private keys from over 20 mainstream encrypted wallets, including MetaMask, Exodus, and Electrum.
Reporting on Iran
The APT35 Dump Episode 4: Leaking The Backstage Pass To An Iranian Intelligence Operation
Domain Tools alleges, based on a supposed leak, that Iranian APT operation are more like The Office than Sneakers.
Seen through this lens, APT35 functions as a government department more than a hacker crew. Someone drafts a VPS requisition; another logs the cost in euros; a supervisor approves the line item; and only then does a technician deploy the phishing kit or C2 beacon. It’s the banality of intrusion, the paperwork of digital espionage. Episode 4 strips away the glamour of zero-days and leaves the logistics in plain view: account creation, invoice reconciliation, crypto transaction IDs as bureaucratic stamps of approval. The same apparatus that once managed oil exports now manages data theft and influence operations. Behind every exploit sits a spreadsheet; behind every “state-sponsored attack,” a purchase order; behind every patriotic slogan, an accounts-payable clerk.
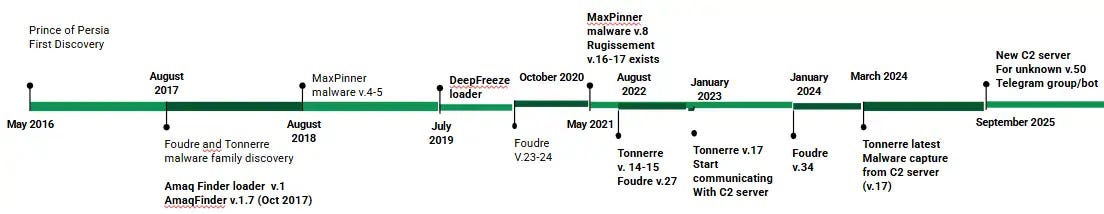
Prince of Persia: A Decade of Iranian Nation-State APT Campaign Activity under the Microscope
Tomer Bar detail this alleged Iranian operation which is noteworthy for using a domain generation algorithm and that the algorithm itself has evolved in order to remain resilient.
The scale of Prince of Persia’s activity is more significant than we originally anticipated. Our research identified multiple campaigns that used a large number of malware variants and C2 servers.
There are at least three active variants of Foudre and Tonnerre using different DGA in parallel and communicating to an active C2 server.
Tonnerre v50—which was detected as recently as September 2025 and uses an unknown DGA algorithm.
Tonnerre v12-16, which uses the original CRC32 based DGA
Tonnerre v17, which uses the original CRC32 as the first stage and then adds a second-stage DGA algorithm
Reporting on Other Actors
GhostPairing Attacks: from phone number to full access in WhatsApp
Luis Corrons and Martin Chlumecký detail an attack technique which appears to be growing in use by a variety of threat actors. It will be interesting to see what Meta/WhatsApp and Signal do to bolster security in response to these techniques becoming widely understood and leveraged.
Gen has discovered a novel WhatsApp account takeover campaign that we refer to as GhostPairing Attack. On the surface it looks very simple. Victims receive a message from one of their contacts…
…
We use the term GhostPairing Attack because the victim is tricked into completing WhatsApp’s own device pairing flow, adding the attacker’s browser as an invisible extra device on their account. There is no password theft or SIM swap – instead, the user approves the attacker themselves by entering a pairing code that looks like normal verification.
https://www.gendigital.com/blog/insights/research/ghostpairing-whatsapp-attack
The giant botnet Kimwolf that infected 1.8 million Android devices worldwide
Alex.Turing, Wang Hao, Acey9 and rootkiter shows the scale of this allegedly Russia based actor run botnet. It is primarily used for DDoS attacks, but the scale if noteworthy irrespective of use.
On December 4th, we observed approximately 1.83 million bot IPs, a historical peak. That day, some of Kimwolf’s normally used C2 servers were shut down by relevant authorities, causing many bots to lose connection to their original C2 servers and instead attempt to connect to our pre-registered C2 servers. This anomaly resulted in a concentrated exposure of more bots within a short period, therefore the data for that day may be closer to the lower limit of the actual infection scale.
The infected devices are distributed across multiple time zones globally. Due to time zone differences and usage habits (such as turning them off at night and not using TV boxes on holidays), these devices are not online simultaneously, further increasing the difficulty of comprehensive observation through a single time window.
There are multiple versions of kimwolf, and the C2 implementations used in these versions are not entirely the same. This is one of the main reasons why we cannot obtain a complete viewpoint.
https://blog.xlab.qianxin.com/kimwolf-botnet/
React2Shell used as initial access vector for Weaxor ransomware deployment
James Tytler and Gavin Hull detail the criminal use of this vulnerability. Interesting also to note that Cobalt Strike continues to be used by some ransomware crews.
S-RM has now observed one financially motivated threat actor use React2Shell as the initial access vector in a ransomware attack.
..
The specific ransomware payload we observed was a strain called Weaxor, which was first detected in late 2024. Weaxor is reported to be a rebrand of Mallox ransomware strain. Mallox was active from 2021 and associated with exploiting insecure Microsoft SQL servers.
..
Immediately after the threat actor gained access to our client’s network on 5 December 2025, they ran an obfuscated PowerShell command, which established command and control (C2) by downloading a Cobalt Strike PowerShell stager and installing a beacon that called back to their remote infrastructure. After this, the threat actor disabled real time protection on Windows Defender Antivirus to prepare the environment for secondary payloads.
When adversaries bring their own virtual machine for persistence
Tony Lambert and Chris Brook detail an interesting attack chain which is noteworthy due to the use of a distraction technique as well the VM in order to circumvent existing on device EDR.
In this scenario, the adversary wasted no time. After flooding the inbox, they initiated a call to the organization posing as a technical support representative. Their offer was simple: help alleviate the deluge. It’s a calculated maneuver, leveraging distress to gain trust.
After gaining the user’s confidence, the adversary leveraged remote assistance software Quick Assist. This legitimate, built-in Windows application allows a trusted person to take control of another computer remotely.
Instead of directly dropping ransomware or a standard backdoor, the adversary used the Quick Assist foothold to introduce their own VM

https://redcanary.com/blog/threat-intelligence/email-bombing-virtual-machine/
Black Hole of Trust: SEO Poisoning in Silver Fox’s Space
Odyssey
Dillon Ashmore and Asher Glue detail an interesting campaign which is noteworthy for the use of Search Engine Optimisation (SEO) to support initial access. Also the potential false flag attempt..
[We] identified an exposed link management panel used by Silver Fox to track download activity for backdoor installer applications, including Microsoft Teams, revealing operational details and campaign telemetry.
Analysis of the panel and related infrastructure uncovered a broader campaign that supports ReliaQuest’s assessment of a false-flag operation, where Silver Fox employed Cyrillic file names to impersonate a Russian-speaking threat actor.
Silver Fox leveraged SEO poisoning to distribute backdoor installers of at least 20 widely used applications, including communication tools, VPNs, and productivity apps. These primarily target Chinese-speaking individuals and organisations in China, with infections dating back to July 2025 and additional victims across AsiaPacific, Europe, and North America.
All observed samples delivered malware consistent with ValleyRAT’s behaviour, a modular Remote Access Trojan linked to Silver Fox, with supporting infrastructure hosted in Asia.
This research reinforces prior industry guidance: organisations with Chinesespeaking employees or operations in China, regardless of sector, face elevated risk from this campaign.
Discovery
How we find and understand the latent compromises within our environments.
Hunting for Mythic in network traffic
Valery Akulenko and Dmitry Sabadash details how using network traffic analysis it is possible to detect the use of the Mythic C2, even in situations where you can not decrypt TLS.
If Discord usage is permitted on the network and there is no capability to decrypt traffic, it becomes nearly impossible to detect agent activity. In this scenario, behavioral analysis of requests to the Discord server may prove useful. Below is network traffic showing frequent TLS connections to the Discord server, which could indicate commands being sent to an agent.
..
In this case, we can use a Suricata rule to detect the frequent TLS sessions with Discord servers:
https://securelist.com/detecting-mythic-in-network-traffic/118291/
unKover
eversinc33 releases unKover which shows off an interesting technique which could be good to see ported to Volatility.
Windows anti-rootkit driver that can detect drivers mapped to kernel memory. Think Moneta, but for the kernel (obviously this is a simplified comparison). Additionally detects hidden threads as of the latest version.
https://github.com/eversinc33/unKover
Detecting malicious pull requests at scale with LLMs
Callan Lamb, Christoph Hamsen, Julien Doutre, Jason Foral and Kassen Qian show the potential of value of AI in order to detect to malicious code changes. It will be interesting to see as this roles out to their customers if the false/true positive ratios sustain at 0.03% to make it practical.
[We] share how our SDLC Security team built a large language model (LLM)-powered system that reviews every PR at Datadog in real time for malicious activity. You’ll learn how we:
Improved accuracy using prompt engineering and data tuning
Worked around model degradation caused by context limits
Continuously test our tool against real-world exploits, such as the tj-actions and Nx attacks
Along the way, we’ll share what worked, what didn’t, and what we learned about making LLMs useful for large-scale code security.
…
In our early prototypes—built fast, with little data curation—we saw an unsustainable false positive rate of over 10%. Over the next six months, we drove that number down to below 0.03% by focusing on five areas
https://www.datadoghq.com/blog/engineering/malicious-pull-requests/
Detecting Unauthenticated AWS OSINT: Catching Adversaries Before They’re Inside
Rad details how strategic placement of honey buckets can provide a signal that an adversary may be performing recognisance against your organisation.
At the start of most Red Team engagements, we perform OSINT against the target. Public S3 buckets, exposed resources, anything that helps build an initial picture. Finding misconfigurations early is the goal. Unauthenticated cloud enumeration has always been low-risk, there’s no question about it - there’s no authentication, more often than not no logs we’d typically see, nothing to alert on.
That changes with honey buckets as tokens. Deploy them matching your organization’s naming patterns, and you’ll know when someone’s looking - perhaps the earliest detection point in the kill chain.
https://deceptiq.com/blog/detecting-unauth-aws-osint
Agentic Threat Hunting Framework (ATHF)
Sydney releases this framework and shows the potential application of agentic approaches to threat hunting in reality.
The Agentic Threat Hunting Framework (ATHF) is the memory and automation layer for your threat hunting program. It gives your hunts structure, persistence, and context - making every past investigation accessible to both humans and AI.
ATHF works with any hunting methodology (PEAK, TaHiTI, or your own process). It’s not a replacement; it’s the layer that makes your existing process AI-ready.
ATHF provides structure and persistence for threat hunting programs. It’s a markdown-based framework that:
Documents hunts using the LOCK pattern (Learn → Observe → Check → Keep)
Maintains a searchable repository of past investigations
Enables AI assistants to reference your environment and previous work
Works with any SIEM/EDR platform
https://github.com/Nebulock-Inc/agentic-threat-hunting-framework
Defence
How we proactively defend our environments.
BpfJailer: eBPF Mandatory Access Control
Liam Wisehart teases with these slides as I have not be able to find the release of code.
BpfJailer can operate in both a path based (involuntary), and non path based mode (voluntary)
Covers full range of features, including features not present in other MAC solutions
Signed binaries
Proxying/Protocol interception
eBPF implementation allows development to move quickly and safely without changing upstream
No measurable performance regressions across any workload/host type
https://lpc.events/event/19/contributions/2159/attachments/1833/3929/BpfJailer%20LPC%202025.pdf
Microsoft baseline security mode for Office, SharePoint, Exchange, Teams, and Entra
Microsoft includes baseline security mode..
Baseline Security Mode centralizes Microsoft’s recommended security standards for Office, SharePoint, Exchange, Teams, and Entra. Rolling out from November 2025 to March 2026, it provides admins with a dashboard to assess and improve security posture using impact reports and risk-based recommendations, with no immediate user impact.
https://mc.merill.net/message/MC1193689
Incident Writeups & Disclosures
How they got in and what they did.
Hack Reveals the a16z-Backed Phone Farm Flooding TikTok With AI Influencers
Emanuel Maiberg reports
A hacker gained control of a 1,100 mobile phone farm powering covert, AI-generated ads on TikTok.
Doublespeed, a startup backed by Andreessen Horowitz (a16z) that uses a phone farm to manage at least hundreds of AI-generated social media accounts and promote products has been hacked. The hack reveals what products the AI-generated accounts are promoting, often without the required disclosure that these are advertisements, and allowed the hacker to take control of more than 1,000 smartphones that power the company.
The hacker, who asked for anonymity because he feared retaliation from the company, said he reported the vulnerability to Doublespeed on October 31. At the time of writing, the hacker said he still has access to the company’s backend, including the phone farm itself. Doublespeed did not respond to a request for comment.
Vulnerability
Our attack surface.
Abandoned Python Bootstrap Scripts Open the Door to Domain Takeovers Across Multiple PyPI Packages
CyberSRC highlight once again why expired DNS domains provide a rich source of attack surface to organisations of any size.
A newly uncovered software-supply-chain threat is impacting the Python ecosystem: legacy bootstrap scripts embedded in multiple PyPI packages are creating a domain-takeover attack surface, enabling adversaries to hijack installation flows, inject malicious payloads, and execute arbitrary commands on developer machines.
These outdated bootstrap mechanisms rely on hardcoded URLs, expired domains, and abandoned hosting endpoints that attackers can easily re-register and exploit, turning common Python package installations into an RCE delivery pipeline.
MicroSpark: Testing Voltage Glitches on Intel Microcode
Federico Cerutti, Alvise de Faveri Tron and Cristiano Giuffrida perform some awesome research here against modern CPUs highlighting why you will want strong physical controls against your most trusted assets and why deploying things ‘to the edge’ make them hard to secure.
In this work, we present a robust and reproducible experimental platform that pairs a low-cost glitcher with a corebootbased environment on a “Red Unlocked” Intel Goldmont SoC. Leveraging the low-noise execution environment provided by this setup, as well as the possibility of crafting custom microcode routines due to Red Unlock, we successfully identified previously undocumented fault types, including instruction skips at both the architectural and microarchitectural levels on Apollo Lake CPUs. This provides a foundation for future investigations into Intel microcode security, and the potential for broader applications across various CPU models.
https://download.vusec.net/papers/microspark_uasc26.pdf
Vulnhalla: Picking the true vulnerabilities from the CodeQL haystack
Simcha Kosman
By layering an LLM on top of CodeQL, we significantly reduce the overwhelming noise of false positives that typically buries security teams. The result is a workflow where developers and security researchers can focus only on findings that have genuine potential to be exploited.
This approach led us to create Vulnhalla, a tool that allows only the “true and brave” issues to pass through its gates. Using Vulnhalla, in just two days of work and with a budget of under $80, we identified the following vulnerabilities:
CVE-2025-38676 (Linux Kernel),
CVE-2025-0518 (FFmpeg),
CVE-2025-27151 (Redis),
CVE-2025-8854 (Bullet3),
CVE-2025-9136 (RetroArch),
CVE-2025-9809 (Libretro),
CVE-2025-9810 (Linenoise).
… and we continue to find new leads
Remote code execution via ND6 Router Advertisements
FreedBSD whoops..
rtsold(8) and rtsol(8) are programs which process router advertisement packets as part of the IPv6 stateless address autoconfiguration (SLAAC) mechanism.
The rtsol(8) and rtsold(8) programs do not validate the domain search list options provided in router advertisement messages; the option body is passed to resolvconf(8) unmodified.
resolvconf(8) is a shell script which does not validate its input. A lack of quoting meant that shell commands pass as input to resolvconf(8) may be executed.
https://www.freebsd.org/security/advisories/FreeBSD-SA-25:12.rtsold.asc
Offense
Attack capability, techniques and trade-craft.
Third Eye
Matěj Štágl releases this tool which can capture screens/windows on Windows which are intended to not be capturable using some clever tricks.
Usermode
WDA_MONITOR/WDA_EXCLUDEFROMCAPTUREbypasser using undocumented Windows functions.
https://github.com/lofcz/thirdeye
Malware Just Got Its Free Passes Back!
klezVirus plays the next move in the grand game of cyber chess. EDR vendors have taken to call stack analysis to flag malicious activity. klezVirus has refined the spoofing technique.
a PoC to extend FullMoon, which will allow us not only to spoof the call stack to our call, hiding the real origin of the call during the program execution, but also avoid several indicators and traces usually left with the adoption of Moonwalking. Finally, we’ll show out it is possible to refine the technique not only to spoof the stack at every call, but also encrypt our malware while executing virtually any target Windows API.
https://klezvirus.github.io/posts/Moonwalk-plus-plus/
Access granted: phishing with device code authorization for account takeover
The Proofpoint Threat Research Team highlight what others have seen and cause me to remind you call that device codes are passwords by another name..
Proofpoint is tracking multiple threat clusters - both state-aligned and financially-motivated - that are using various phishing tools to trick users into giving access to M365 accounts via OAuth device code authorization.
Successful compromise leads to account takeover, data exfiltration, and more.
Threat actors are using the OAuth 2.0 device authorization grant flow to compromise Microsoft 365 user accounts by approving access for various applications.
Smallest SSHD backdoor
The Hackers Choice provide an SSHD backdoor that detection engineering and forensic teams will want to ensure coverage of.
Survives
apt updateDoes not create any new file.
Does not use
authorized_keysor PAM.
https://github.com/hackerschoice/thc-tips-tricks-hacks-cheat-sheet?tab=readme-ov-file#backdoor-sshd
Sigdream
k0zmer releases this for Linux which detection engineers will want to ensure they can detect the usage of.
sigreturn-oriented programming (SROP) based sleep obfuscation proof of concept for Linux..
a cursed sigreturn-oriented programming (srop) based sleep obfuscation for Linux that encrypts PT_LOAD segments + heap
https://github.com/kozmer/sigdream
Exploitation
What is being exploited..
Multiple Threat Actors Exploit React2Shell
Aragorn Tseng, Robert Weiner, Casey Charrier, Zander Work, Genevieve Stark and Austin Larsen add reporting around the mass exploitation of this vulnerability.
GTIG has identified distinct campaigns leveraging this vulnerability to deploy a MINOCAT tunneler, SNOWLIGHT downloader, HISONIC backdoor, and COMPOOD backdoor, as well as XMRIG cryptocurrency miners, some of which overlaps with activity previously reported by Huntress. These observed campaigns highlight the risk posed to organizations using unpatched versions of React and Next.js.
Malicious SSO Logins on FortiGate Devices Following Disclosure of CVE-2025-59718 and CVE-2025-59719
Arctic Wolf Labs detail in the wild exploitation of this vulnerability and a nuance around the configurations that may enable it to be exploitable.
On December 12, 2025, Arctic Wolf began observing intrusions involving malicious SSO logins on FortiGate appliances. Fortinet had previously released an advisory for two critical authentication bypass vulnerabilities (CVE-2025-59718 and CVE-2025-59719) on December 9, 2025. Arctic Wolf had also sent out a security bulletin for the vulnerabilities shortly thereafter.
These vulnerabilities allow unauthenticated bypass of SSO login authentication via crafted SAML messages, if the FortiCloud SSO feature is enabled on affected Devices. Several product lines were reported to be affected, including FortiOS, FortiWeb, FortiProxy, and FortiSwitchManager.
In their recent advisory, Fortinet stated that FortiCloud SSO login is disabled by default in factory settings. However, when administrators register devices using FortiCare through the GUI, FortiCloud SSO is enabled upon registration unless the “Allow administrative login using FortiCloud SSO” setting is disabled on the registration page.
SonicWall SMA1000 appliance local privilege escalation vulnerability
SonicWall PSIRT detail in the wild exploitation
This vulnerability was reported to be leveraged in combination with CVE-2025-23006 (CVSS score 9.8) to achieve unauthenticated remote code execution with root privileges. CVE-2025-23006 was remediated in build version 12.4.3-02854 (platform-hotfix) and higher versions (released on Jan 22, 2025).
https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2025-0019
Tooling and Techniques
Low level tooling and techniques for attack and defence researchers
Patch Wednesday: Root Cause Analysis with LLMs
Maor Dahan highlights the augmented productivity that LLMs can bring.
In this research, we examined the use of large language models for finding the root cause of patched vulnerabilities.
We developed a multi-agent system called PatchDiff-AI that autonomously analyzes the root cause of Patch Tuesday vulnerabilities and generates a detailed report.
This kind of analysis can help security teams analyze vulnerabilities almost instantly, for either defensive or offensive purposes.
By using multiple strategies, we were able to fine-tune our system to achieve a more than 80% success rate in fully automated report generation, including attack vector analysis and triggering flo
https://www.akamai.com/blog/security-research/patch-wednesday-root-cause-analysis-with-llms
eXtended-Address-Table-Hooking
C5Hackr releases this userland hooking work aid...
XAT is a lightweight, architecture-aware hooking library focused on Address Table manipulation, providing reliable interception of API calls via:
IAT (Import Address Table) patching
Delay-IAT patching (delay-load imports)
EAT (Export Address Table) patching (when safe)
https://github.com/C5Hackr/XATHook
Wirebrowser
Filippo Cavallarin is a top of class web tooling approach developer and Wirebrowser is another example.
Wirebrowser is a debugging, interception, and memory-inspection toolkit powered by the Chrome DevTools Protocol (CDP). It unifies network manipulation, API testing, automation scripting, and deep JavaScript memory inspection into one interface.
With features like Breakpoint-Driven Heap Search and real-time Live Object Search, Wirebrowser provides researchers and engineers with precise, high-visibility tools for client-side analysis, reverse engineering, and complex application debugging.
https://github.com/fcavallarin/wirebrowser
Decompiling run-only AppleScripts
Pepe Berba walks through how to do it..
https://pberba.github.io/security/2025/12/14/decompiling-run-only-applescripts/
How CPU Caches Work
0xkato provides an easy to understand explanation..
This post is a tour of how CPU caches actually work, using a simple real‑world picture: a busy office with desks, cabinets, and a big archive room.
https://www.0xkato.xyz/How-CPU-Caches-Work/
macOS Tahoe 26.2 and RDMA
Just calling out this new feature which is another example of a high-speed interconnect where we lack protective monitoring in the contemporary world.
Enables low-latency communication between Thunderbolt 5 hosts for use cases including distributed AI inference using MLX. (164123391)
Footnotes
Some other small (and not so small) bits and bobs which might be of interest.
Annual, quarterly and monthly reports
Secure connectivity for LEO satellites in the EU - European Parliament
Decision-Making Amid Information-Based Threats in Sociotechnical Systems: A Review
How data science can boost your detection engineering maintenance and keep you from herding sheep
China
Artificial intelligence
AI, intelligence processing, analysis, and decision-making in the Russo-Ukrainian war
Llama-based source code vulnerability detection: Prompt engineering vs Fine tuning
Vulnhalla: Picking the true vulnerabilities from the CodeQL haystack
Weird Generalization and Inductive Backdoors: New Ways to Corrupt LLMs
VulnLLM-R: Specialized Reasoning LLM with Agent Scaffold for Vulnerability Detection
Llama-based source code vulnerability detection: Prompt engineering vs Fine tuning
Penetration Testing of Agentic AI: A Comparative Security Analysis Across Models and Frameworks
Building an Open-Source AI-Powered Auto-Exploiter with a 1.7B Parameter Model: No Paid APIs Required
ToolShell, Patch Bypass, and the AI That Might Have Seen It Coming
Paper2Video: Automatic Video Generation from Scientific Papers
Books
Nothing overly of note this week
Events
Control System Security Conference 2026 - February 10, 2026 - Japan
2nd Microarchitecture Security Conference - February 3, 2026 - Belgium
Finally finally the NCSC’s podcast series.
Unless stated otherwise, linked or referenced content does not necessarily represent the views of the NCSC and reference to third parties or content on their websites should not be taken as endorsement of any kind by the NCSC. The NCSC has no control over the content of third party websites and consequently accepts no responsibility for your use of them.
This newsletter is subject to the NCSC website terms and conditions which can be found at https://www.ncsc.gov.uk/section/about-this-website/terms-and-conditions and you can find out more about how will treat your personal information in our privacy notice at https://www.ncsc.gov.uk/section/about-this-website/privacy-statement.