

Welcome to the weekly highlights and analysis of the blueteamsec (and my wider reading). Not everything makes it in, but the best bits do.
Operationally this week see the warning on Russian aligned hacktivist DDoS group activity against the UK. This is along with reports of exploitation of Cisco unified communications products - “The Cisco PSIRT is aware of attempted exploitation of this vulnerability in the wild.” and Single Sign-on used to compromise Fortinet firewalls - “in the last 24 hours, we have identified a number of cases where the exploit was to a device that had been fully upgraded to the latest release at the time of the attack,”
In the high-level this week:
NCSC issues warning over hacktivist groups disrupting UK organisations and online services - UK NCSC warns - “Russian‑aligned hacktivist groups continue to target UK organisations with disruptive cyber attacks”
Minister Lloyd cyber security speech at BIBA insurance conference - Baroness Lloyd of Effra CBE addresses - “The message is clear: resilience is not just about defence, but about readiness to respond and rebuild. By embedding cyber risk into strategic decision-making and rehearsing recovery plans, businesses can minimise disruption, protect their customers, and safeguard jobs - even in the face of sophisticated attacks.”
Minister Lloyd speech on software security and cyber resilience - Baroness Lloyd of Effra CBE addresses - “This Code outlines the minimum actions that software suppliers should take to ensure a baseline level of security across the software market. But communicating those expectations is just the first step. We now need to ensure that these actions are embedded in UK supply chains to provide businesses with confidence in the technologies they need to operate and to grow.”
2025 CBEST thematic - Bank of England summarise - “The key messages in this publication for firms and FMIs to consider include:
To reduce the likelihood of severe cyberattacks firms and FMIs should look to harden operating systems, including by patching vulnerabilities and securely configuring key applications.
Firms and FMIs can reduce the impact of unauthorised access to sensitive systems and information by strengthening credentials management, enforcing strong passwords, considering the use of multi-factor authentication (MFA), preventing or detecting insecure credential storage, and through appropriate segmentation of networks.
Early detection and effective monitoring, alerting and response processes are key to reducing the impact from cyberattacks.
Firms and FMIs should implement risk-based remediation plans with oversight from risk managers and internal auditors to ensure the successful remediation of technical findings, including vulnerabilities.”
Implementing proactive cyber risk management in the health and social care supply chain - NHS England write - “This is an open letter to all current suppliers to the NHS and the wider health and care system, sent January 2026.” .. “From January 2026, NHS England or the relevant contracting authority may contact suppliers to:
discuss your key cyber security controls, including those set out in the Supply Chain Charter
request supporting information or evidence where appropriate. For example, where the supplier delivers services that are critical to patient care or operational continuity, or where early discussions or risk indicators suggest that further assurance would be helpful. Any requests will be proportionate, will rely on existing assurance wherever possible, and will be made in line with the established responsibilities of NHS England and/or other contracting authorities.”
US National Defence Strategy - Department of War releases - “Deter and Defend Against Cyber Threats. The Department will prioritize bolstering cyber defenses for U.S. military and certain civilian targets. DoW will also develop other options to deter or degrade cyber threats to the U.S. Homeland.” … “We will maintain a robust and modern nuclear deterrent capable of addressing the strategic threats to our country, raise and sustain formidable cyber defenses…”
Poland Stops Cyberattacks on Energy Infrastructure - Chancellery of the Prime Minister Republic of Poland disclose - “Prime Minister Donald Tusk met with ministers, the heads of security services, and institutions responsible for Poland's energy security. The briefing was related to a cyberattack that occurred at the end of last year. Poland successfully defended itself, and there was no blackout or other negative consequences. The incident was nevertheless treated very seriously.”
Cyberattack Targeting Poland’s Energy Grid Used a Wiper - Kim Zetter reports - “A cyberattack that targeted power plants and other energy producers in Poland at the end of December used malware known as a “wiper” that was intended to erase computers and in an operation that was intended to cause a power outage and other disruption to services, says European security firm ESET, which obtained a copy of the malware used in the attack.”
Commission strengthens EU cybersecurity resilience and capabilities - European Commission announces - “The package includes a proposal for a revised Cybersecurity Act, which enhances the security of the EU's Information and Communication Technologies (ICT) supply chains. It ensures that products reaching EU citizens are cyber-secure by design through a simpler certification process. It also facilitates compliance with existing EU cybersecurity rules and reinforces the EU Agency for Cybersecurity (ENISA) in supporting Member States and the EU in managing cybersecurity threats.”
Proposal for a Regulation for the EU Cybersecurity Act - European Commission proposes - “The Proposal for a revised Cybersecurity Act is part of this package. It aims to increase cybersecurity capabilities and resilience and prevent fragmentation across the EU digital single market. It also enhances the security of the EU’s Information and Communication Technologies (ICT) supply chains. It ensures that products reaching EU citizens are cyber-secure by design through a simpler certification process. It also facilitates compliance with existing EU cybersecurity rules and reinforces the EU Agency for Cybersecurity (ENISA) in supporting Member States and the EU in managing cybersecurity threats.”
US Funding on Cyber - United States Senate Committee on Appropriations proposes for CISA - “For necessary expenses of the Cybersecurity and Infrastructure Security Agency for operations and support, $2,218,634,000, which shall be for the purposes and in the amounts specified in the ‘‘Final Bill’’ column for Cybersecurity and Infrastructure Security Agency, Operations and Support in the ‘‘Department of Homeland Security Appropriations Act, 2026’’ table in the explanatory statement described in section 4” .. and others ..
From Gut Feel to Gains: The Cybersecurity ROI Pyramid - Antwerp Management School outline - “Boards and regulators increasingly demand proof that cybersecurity budgets create value, yet most organisations still rely on intuition rather than economic analysis. Building on Antwerp Management School research, this article proposes a pragmatic pyramid model, comprising basic hygiene, compliance imperatives, and targeted risk-driven measures to help organisations apply Return on Security Investment (ROSI) selectively and align cybersecurity spending with business value.”
SSSCIP Specialists Enhance Cyber Incident Response Capabilities Through NATO Training Programme - State Service for Special Communications and Information Protection of Ukraine announce - “The curriculum covered all key phases of cyber incident and attack response: ranging from theoretical instruction to intensive practical exercises, security event detection, and report preparation, factoring in established NIST and ENISA standards.”
Germany Forces Lexus to Remotely Kill Car Heating In Dead Of Winter - Yahoo News reports - an example where Over The Air (OTA) software updates and/or intermediary services can be used to change vehicle functionality post fact.
Vehicle Kill Switch Divides Republicans: What To Know - News Week reports - “Introducing or even mandating kill switch technology has been divisive, with critics seeing it as government overreach and those in favor seeing it as potentially lifesaving. Debate has also focused on different perspectives of what the technology can and cannot do, such as tracking a person’s driving and location.”
Epistemic Security for Crisis Resilience - Demos think tank - “An analysis of information threats, vulnerabilities, and priority interventions for the maintenance of effective crisis response capacity in democratic societies”
Interpretation of “internet-connected radio equipment” under the Radio Equipment Directive (RED) - European Commission clarifies - “This document does not address the Cyber Resilience Act, but focuses exclusively on the analysis of one category of radio equipment covered by Delegated Regulation (EU)
2022/30, namely “internet-connected radio equipment”
The Central Bank of Iran has acquired US dollar stablecoins worth at least half a billion dollars - Elliptic reports - “There are indications that the acquired USDT was used to support the value of the Iranian Rial, providing a viable alternative for market intervention given that sanctions prevent the regime from deploying its official foreign reserves.”
Reporting on/from China
Strategic Snapshot: Russia–PRC Technology and Hybrid Operations - James Town snapshot - “The PRC’s reorganized Cyberspace Force recently displayed command and control, reconnaissance and sensing, and cyber-electromagnetic countermeasures equipment at a parade commemorating the end of World War II. This included a new UAV data relay system, a data spectrum monitoring vehicle, a signal-jamming vehicle, an electromagnetic reconnaissance and jamming vehicle, a network communication node vehicle, and an information jamming vehicle. These upgrades suggest that the PLA has learned lessons from shortcomings in information and electronic warfare during the Russian invasion of Ukraine.”
Beijing tells Chinese firms to stop using US and Israeli cybersecurity software, sources say - Reuters reports (forgot to include last week) - “China bans use of software from Palo Alto Networks, CrowdStrike, and several others, sources say .. Alphabet’s Mandiant, Thales’ Imperva, Wiz, SentinelOne, Rapid7 also on cyber blacklist”
Rishi Sunak: Xi hacks for secrets, Kim for cash, Putin for chaos - The Times op eds - “When I discussed this issue with leaders of the Five Eyes security alliance — the US, UK, Canada, Australia and New Zealand — what struck us was how our adversaries’ use of hacking reveals their intentions. The Chinese are focused on the long game, using it for espionage and pre-positioning.”
Brussels in move to bar Chinese suppliers from EU’s critical infrastructure - The Financial Times reports - “Brussels is to propose phasing out Chinese-made equipment from critical infrastructure in the EU, barring companies such as Huawei and ZTE from telecommunications networks, solar energy systems and security scanners, according to officials.”
Tianfu Cup is back this year..
AI
On the Coming Industrialisation of Exploit Generation with LLMs - Sean Heelan experiments - “With the next major release from a frontier lab I would love to read something like “We spent X billion tokens running our agents against the Linux kernel and Firefox and produced Y exploits“. It doesn’t matter if Y=0. What matters is that X is some very large number.”
Anamnesis: LLM Exploit Generation Evaluation related - “This repository contains the evaluation framework for studying how LLM agents generate exploits from vulnerability reports in the presence of exploit mitigations. Given a bug report and proof-of-concept trigger, agents analyze vulnerable software and produce working exploits that bypass various security mitigations.”
Toward Risk Thresholds for AI-Enabled Cyber Threats: Enhancing Decision-Making Under Uncertainty with Bayesian Networks - UC Berkley Center for Long-Term Cybersecurity proposes - “[We] propose a structured approach for developing and evaluating AI cyber risk thresholds. Their approach relies on the use of Bayesian networks (BNs), a type of probabilistic modeling tool that can help determine thresholds by integrating a wide range of information about both the world and AI systems” - should also be augmented by looking out the window..
Agent Skills in the Wild: An Empirical Study of Security Vulnerabilities at Scale - Tianjin University, Southern Cross University and Nanyang Technological University publish - “Our findings reveal pervasive security risks: 26.1% of skills contain at least one vulnerability, spanning 14 distinct patterns across four categories—prompt injection, data exfiltration, privilege escalation, and supply chain risks.”
Comparing the Secure Coding Capabilities of Popular Coding Agents - Ori David assesses - “all agents introduced a significant amount of vulnerabilities across the different applications. Codex, Cursor and Replit tied for first place with a total of 13 vulnerabilities, while Claude Code came in last with 16 vulnerabilities. In addition to introducing the most vulnerabilities overall, Claude Code also had the highest number of critical-severity findings.”
Sigma Detection Classification - Cotool benchmark - “This benchmark evaluates LLMs' intrinsic knowledge of detection engineering and the MITRE ATT&CK framework. Unlike agentic tasks where models can query external resources, this single-turn classification task tests what models have learned about adversary tradecraft during training.”
Claude Magic String Denial of Service - Nick Frichette builds on research by Austin Parker and Lizzie Moratti - “Anthropic documents a “magic string” that intentionally triggers a streaming refusal. Starting with Claude 4 models, streaming responses return
stop_reason: "refusal"when streaming classifiers intervene, and no refusal message is included. This test string exists so developers can reliably validate refusal handling, including edge cases like partial output and missing refusal text. That makes it a great QA tool, but it also creates a predictable failure mode. If an attacker can inject the string into any part of the prompt context, they can reliably force refusals, potentially creating a sticky, low-effort denial of service until the context is reset.” - integrators beware!The AI ecosystem: managing fragility and building resilience - Global Security and Innovation Summit ponder - “Data access is becoming increasingly uneven. The amount of data produced worldwide continues to grow rapidly, but access to the high-quality, large-scale datasets needed to train advanced AI models is narrowing. Large, vertically integrated firms such as Amazon and Google generate, collect and control vast proprietary datasets through their search, retail and cloud platforms, giving them a structural advantage over smaller players.”
S. Korea becomes 1st nation to enact comprehensive law on safe AI usage - Yonhap News Agency reports - “In detail, the act introduces the concept of "high-risk AI," referring to AI models used to generate content that can significantly affect users' daily lives or their safety, including applications in the employment process, loan reviews and medical advice.”
Cyber proliferation
Spain closes Pegasus spyware probe again, saying Israel has not responded - Reuters reports - “The investigation was launched after the Spanish government disclosed in 2022 that NSO's spyware had been used to spy on members of the Spanish cabinet, sparking a political crisis that led to the resignation of the country's spy chief.”
From Protest to Peril Cellebrite Used Against Jordanian Civil Society - Citizen Lab report - “Cellebrite’s products have been used by the Jordanian authorities to extract data from the phones of activists and civil society members without their consent. During our forensic investigation of devices that were seized by authorities and returned to their owners, we uncovered iOS and Android Indicators of Compromise (IoCs) that we attribute with high confidence to Cellebrite’s forensic extraction products.”
Bounty Hunting
Greece Arrests Chinese SMS Blaster Scammers - CommsRisk reports - “The arrests in Greece relied upon dumb luck rather than technologies that identify and pinpoint fake base stations. An employee of a shopping mall in Spata, an eastern district of Athens, warned police that two Chinese customers had behaved suspiciously.”
Jordanian Man Admits Selling Unauthorized Access to Computer Networks of 50 Companies - US Department of Justice announces - “In May 2023, law enforcement officers were investigating an online forum where malware and malicious code was being offered for sale. Albashiti controlled an online moniker named “r1z” and used it in the online forum. On May 19, 2023, Albashiti sold to an undercover law enforcement officer unauthorized access to the networks of at least 50 victim companies in exchange for cryptocurrency.”
Venezuelan Nationals Convicted in ATM Jackpotting Scheme to Be Deported - US Department of Justice announces - “The defendants would approach an ATM at nighttime and remove the outer casing of the machine and then connect a laptop computer to install malware which overcame the ATM’s security protocols.”
Singapore court rejects application by Chinese suspect wanted in US for global malware crimes - Channel News Asia reports - “The US Government alleged that Wang had been involved in developing and distributing malicious software with the intent to infect residential computers worldwide, selling access to Internet Protocol addresses that were associated with the network of compromised computers.”
Market Incentives
FTC Announces 10-Year Information Security Consent Orders with Illuminate Education and Illusory Systems - FTC announced in December - “The proposed complaint alleges that Respondent claimed to keep users’ assets secure, but in fact failed to implement reasonably secure software development practices. For example, the proposed complaint alleges that Respondent failed to: conduct adequate unit tests, implement a process for receiving and addressing third-party security vulnerability reports, have a Written Information Security Plan, and implement widely-known technologies that would mitigate critical loss of user funds.”
Coupang investors seek US probe over South Korea’s handling of data leak - Reuters reports - “The move comes after Coupang reported in November that personal data for some 33 million customers in South Korea were compromised, triggering a backlash from lawmakers and the public, which prompted a wide-ranging investigation as well as lawsuits from investors and consumers.” .. ““The investors said they have asked the U.S. Trade Representative (USTR) to investigate South Korea’s actions and impose "appropriate trade remedies, potentially including tariffs and other sanctions," arguing that the response to the breach has gone far beyond normal regulatory enforcement.”
The State of Vulnerability Disclosure Policy Usage in Global Consumer IoT in 2025 - IoT Security Foundation publish - “This year’s data highlights emerging patterns in how vulnerability disclosure is being implemented. More companies are referencing regulation directly, some formalising practices under Coordinated Vulnerability Disclosure (CVD), while others use third-party platforms or proxy services to manage reports. Regional differences are softening as legislation converges globally, but smaller vendors and newer market entrants still lag far behind public expectations.”
CrowdStrike defeats shareholder lawsuit over huge software outage - Yahoo! Finance reports - “A federal judge dismissed a lawsuit by CrowdStrike shareholders who said the cybersecurity company defrauded them by concealing its inadequate software testing and quality assurance procedures, before a July 2024 outage crashed more than 8 million Microsoft Windows-based computers worldwide.”
SK Telecom files legal challenge to record $91M fine after data leak - Korea JoonAng Daily reports - “SKT said its 1.2 trillion won package, intended to compensate consumers and invest in security, alongside the absence of reported financial incidents, should be accounted for when calculating the fine.”
Reflections this week are around the importance of context along with observations and nuanced messaging.
This week we had Evidence That the Era of Advanced AI-Generated Malware Has Begun and KONNI Adopts AI to Generate PowerShell Backdoors.
These disclosures led to the headlines VoidLink Linux Malware Framework Built with AI Assistance Reaches 88,000 Lines of Code, Complex VoidLink Linux Malware Created by AI and Konni hackers target blockchain engineers with AI-built malware among many others.
Some of these may conjure up images of AI choosing entirely autonomously how to develop the malware. The reality is however more nuanced - that is human expertise was is in reality used to drive both.
In the case of the first, we see:
Artifacts from VoidLink’s development environment suggest that the developer followed a similar pattern: first defining the project based on general guidelines and an existing codebase, then having the AI translate those guidelines into an architecture and build a plan across three separate teams, paired with strict coding guidelines and constraints, and only afterward running the agent to execute the implementation.
The # of lines of code (88,000 in this instance) whilst interesting is not indicator of value. I say this has someone who wrote what a colleague once called a stegosaurus function.
In the case of the second we see:
The PowerShell backdoor strongly indicates AI-assisted development rather than traditional operator-authored malware.
The context is that it should come as no surprise that developer productivity enhancers are leveraged both by those who wish to do good as well as bad. So yes, whilst AI has accelerated the development human expertise on what is of use, approaches etc. are, for now at least, still important…
Not getting this via email? Subscribe:
Think someone else would benefit? Share:
All attribution is by others and not the UK Government unless specifically stated as such, please see the legal text at the end.
Have a lovely Sunday…
Ollie
Cyber threat intelligence
Who is doing what to whom and how allegedly.
Reporting on Russia
Gamaredon: Now Downloading via Windows Updates Best Friend “BITS”
Robin Dost details this alleged Russian tradecraft shift which will be of note to defence teams who want to be in a position to detect. Important to also note that initial access has not changed.
From a delivery perspective, not much has changed compared to Gamaredons last shift. The victim still receives a RAR archive as an attachment. When opened or extracted, it drops an HTA file into the Startup folder, infecting the system on the next reboot.
https://blog.synapticsystems.de/gamaredon-now-downloading-via-windows-updates-best-friend/
Reporting on China
Weaponized in China, Deployed in India: The SyncFuture Espionage Targeted Campaign
eSentire detail this alleged Chinese operation which shows basic initial access tradecraft and value of software execution controls to mitigate such accesses but the importance of ensuring coverage.
The campaign targets residents of India with phishing emails that impersonate the Income Tax Department of India, luring victims into downloading a malicious archive. The threat actor’s primary objective is to gain persistent, elevated access to the victim’s machine for continuous monitoring of user activities, file operations, and exfiltration of sensitive information.
The infection chain demonstrates a high level of sophistication, beginning with a DLL side-loading technique where a legitimate, signed Microsoft application is used to load a malicious DLL. This initial loader is equipped with extensive anti-debugging and anti-analysis checks to thwart inspection.
Upon successfully passing these checks, the malware contacts a Command-and-Control (C2) server to download a packed shellcode. This second stage unpacks itself in memory and employs two key methods for privilege escalation and defense evasion:
What's in the box !?
NetAskari analyse the tooling from one alleged Chinese individual in order to shed some light of their enablers.
[We] got access to a little "toolbox" of a Chinese red-team/pen-tester.
We are not suggesting, of course, that these software packages are explicitly used by APTs or sophisticated state-backed hackers in China. Rather, they offer a small but useful overview of what the “foot soldiers” might bring to the table.
One more interesting find was a copy of Godzilla. A webshell / exploit framework that has been used in a series of attacks in 2021 on US infrastructure and was on the radar of CISA and DHS.
substack.com/inbox/post/184574472
Reporting on North Korea
Operation Poseidon: Spear-Phishing Attacks Abusing Google Ads Redirection Mechanisms
Genians detail this alleged North Korean operation which is noteworthy for a number of reasons. Namely the use of compromised legitimate websites to host parts of their campaigns, advertising URLs and more. The attempt to blend in for operational security reasons show they are at least thinking about it..
A spear phishing campaign disguised as advertising URLs was used to bypass security filtering mechanisms and user awareness
Poorly secured WordPress websites were abused as malware distribution points and C2 infrastructure
“Poseidon” was identified as an internally named and operated attack operation unit attributed to the Konni APT
The EndRAT malware was loaded through the execution of an AutoIt script masquerading as a PDF file
EDR responses providing behavior-based endpoint detection are essential
https://www.genians.co.kr/en/blog/threat_intelligence/spear-phishing
PurpleBravo’s Targeting of the IT Software Supply Chain
Insikt Group® runs onto the pitch with their analysis of this now well understood alleged North Korean campaign. The sectoral victimology will be of interest although twenty organisations seems on the small size.
PurpleBravo employs a combination of fictitious personas, organizations, and websites to distribute malware to unsuspecting job seekers in the software development industry. Candidates sometimes use their corporate devices, thereby compromising their employers’ security.
PurpleBravo uses a variety of custom and open-source malware and tools in its operations, including BeaverTail, InvisibleFerret, GolangGhost, and PylangGhost.
[We] identified 3,136 individual IP addresses linked to likely targets of PurpleBravo activity and twenty potential victim organizations in the AI, cryptocurrency, financial services, IT services, marketing, and software development industries.
Insikt Group has observed multiple points of overlap between PurpleBravo and PurpleDelta, Recorded Future’s designation for North Korean IT workers, indicating that some individuals may be active in both operations.
PurpleBravo’s heavy targeting of the IT and software development industries in South Asia presents an overlooked and acute supply-chain risk to organizations that contract or outsource their IT services work.
https://www.recordedfuture.com/research/purplebravos-targeting-it-software-supply-chain
MoonPeak malware executed via LNK files
IIJ Sect in Japan reports on this alleged North Korean operation which takes us back to the time of lnk usage in initial access. Once again appears financially motivated.
In January 2026, IIJ observed a malicious LNK file that executed malware believed to have been used in attacks targeting users in South Korea. Malware analysis revealed that the LNK file was used to execute MoonPeak (a variant of the XenoRAT malware), a malware used by a threat actor1 believed to be affiliated with North Korea (DPRK) .
Judging from the file name, this LNK file may have been used in attacks by North Korea targeting South Korean investors in order to obtain foreign currency
https://sect.iij.ad.jp/blog/2026/01/dprk-moonpeak-executed-via-malicious-lnk-file/
How to Get Scammed (by DPRK Hackers)
Oz provides their approach and breakdown of the campaign by many names allegedly originating from North Korea. Again it shows diversity in infrastructure and approach for what is apparently a financially motivated attacker.
The scammer’s approach and social engineering tactics
How to safely analyze suspicious code
The malware itself (spoiler: blockchain as a dropper — yes, really)
The full kill chain from obfuscated JS to the final payload
https://medium.com/@0xOZ/how-to-get-scammed-by-dprk-hackers-b2f7588aea76
Threat Actors Expand Abuse of Microsoft Visual Studio Code
Thijs Xhaflaire details an alleged evolution in North Korean initial access tradecraft which will be of note to those of you who are responsible for defending developer heavy environments. Watch them git clones…
Earlier this week, [we] identified another evolution in the campaign, uncovering a previously undocumented infection method. This activity involved the deployment of a backdoor implant that provides remote code execution capabilities on the victim system.
In this campaign, infection begins when a victim clones and opens a malicious Git repository, often under the pretext of a recruitment process or technical assignment. The repositories identified in this activity are hosted on either GitHub or GitLab and are opened using Visual Studio Code.
https://www.jamf.com/blog/threat-actors-expand-abuse-of-visual-studio-code/
Reporting on Iran
Handala The Move to Starlink
CheckPoint Research alleged that the Iran internet shutdown forced some of the in country teams to move to Startlink
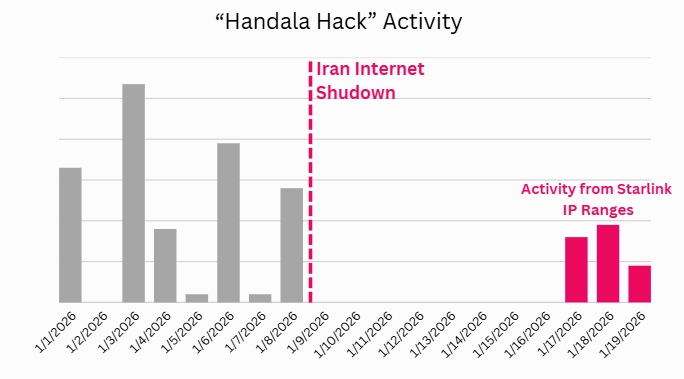
x.com/_CPResearch_/status/2013349461070586054?s=20
Inside Iran’s APT Network: Profiling the Most Active Iranian State‑Linked Threat Actors
Falconfeeds provides a summary based on the analysis of the work of many of alleged Iranian state linked cyber actors.
The following sections detail the organizational structures, technical tradecraft, and campaign histories of these actors, providing a strategic baseline for defense industrial base (DIB), government, and critical infrastructure stakeholders.
Reporting on Other Actors
Scattered Spider Attacks | Infrastructure and TTP Analysis
Will Thomas provides a valuable analysis and this important conclusion..
The shared nature of Scattered Spider’s infrastructure means that a single IP address is no longer a reliable indicator of intent. To a standard firewall, a login from a residential IP or a connection to a tunneling service looks like business as usual. Context is the only differentiator. Behavioral analytics moves the goalposts for the adversary by focusing not on what the infrastructure is, but how it is being used and who it truly belongs to. This is where Team Cymru transforms raw network noise into actionable intelligence.
https://www.team-cymru.com/post/scattered-spider-attacks-infrastructure-profile
Operation Nomad Leopard: Targeted Spear-Phishing Campaign Against Government Entities in Afghanistan
Sathwik Ram Prakki details a regional campaign which uses phishing by a rather clumsy adversary. Noteworthy for the regional focus..
The SEQRITE Labs APT Team has been analyzing threats across different regions and recently started tracking a threat group that is targeting Afghan government employees. The attackers are using a fake lure that mimics an official government document to target ministries and administrative offices. In this blog, we explain the complete infection chain used in this campaign along with operational security mistakes made by the actor. We also highlight how the attacker paid attention to small details in the document, making it look like a genuine Afghan government notice.
Phishing kits adapt to the script of callers
Okta Threat Intelligence details hybrid nature of capability which is able to leverage voice direction in sync with browser in order to circumvent MFA. Or put another way it writes the business case for phishing resistant (FIDO) solutions such as passkeys.
These custom kits are made available on an as-a-service basis and are increasingly used by a growing number of intrusion actors targeting Google, Microsoft, Okta and a range of cryptocurrency providers.
The kits are capable of intercepting the credentials of targeted users, while also presenting the supporting context required to convince users to approve MFA challenges, or to take other actions in the interests of the attacker on the phone. They can be adapted on the fly by callers to control what pages are presented in the user’s browser, in order to sync with the caller’s script and whatever legitimate MFA challenges the caller is presented with as they attempt to sign-in.
The phishing kits appear, based on common features, to have evolved from the same lineage to specifically meet the needs of callers that are interacting with targeted users in real-time.
The most critical of these features are client-side scripts that allow threat actors to control the authentication flow in the browser of a targeted user in real-time while they deliver verbal instructions or respond to verbal feedback from the targeted user. It’s this real-time session orchestration that delivers the plausibility required to convince the threat actor’s target to approve push notifications, submit one time passcodes (OTP) or take other actions the threat actor needs to bypass MFA controls.
https://www.okta.com/blog/threat-intelligence/phishing-kits-adapt-to-the-script-of-callers/
Browser Extensions Gone Rogue: The Full Scope of the GhostPoster Campaign
Natalie Zargarov details a campaign and sheds light not only of the scale (800k) but also the age (5+ years). This reporting gives a sense as to how threats in complex eco-systems can go undetected for some time.
Last month, researchers at Koi Security published a detailed analysis of a malicious Firefox extension they dubbed GhostPoster – a browser-based malware leveraging an uncommon and stealthy payload delivery method: steganography within a PNG icon file. This innovative approach allowed the malware to evade traditional extension security reviews and static analysis tools.
Following their publication, our investigation identified 17 additional extensions associated with the same infrastructure and tactics, techniques, and procedures (TTPs). Collectively, these extensions were downloaded over 840,000 times, with some remaining active in the wild for up to five years.
5 Malicious Chrome Extensions Enable Session Hijacking in Enterprise HR and ERP Systems
Kush Pandya details a campaign which is interest for a number of reasons. First is the approach and second is the focus. You can see how a user may be convinced to deploy..
[We] identified five malicious Chrome extensions targeting enterprise HR and ERP platforms including Workday, NetSuite, and SuccessFactors. The extensions work in concert to steal authentication tokens, block incident response capabilities, and enable complete account takeover through session hijacking. Four extensions are published under the name
databycloud1104, while the fifth operates under different brandingsoftwareaccessbut shares identical infrastructure patterns. Combined, these extensions have reached over 2,300 users.The campaign deploys three distinct attack types: cookie exfiltration to remote servers, DOM manipulation to block security administration pages, and bidirectional cookie injection for direct session hijacking.
https://socket.dev/blog/5-malicious-chrome-extensions-enable-session-hijacking
Dissecting CrashFix: KongTuke’s New Toy
Anna Pham, Tanner Filip and Dani Lopez detail an operation which again shows the misuse of browser extensions to facilitate initial access.
[We] observed threat actors using a malicious browser extension to display a fake security warning, claiming the browser had “stopped abnormally” and prompting users to run a “scan” to remediate the threats.
Our analysis revealed this campaign is the work of KongTuke, a threat actor we have been tracking since the beginning of 2025. In this latest operation, we identified several new developments: a malicious browser extension called NexShield that impersonates the legitimate uBlock Origin Lite ad blocker, a new ClickFix variant we have dubbed “CrashFix” that intentionally crashes the browser then baits users into running malicious commands, and ModeloRAT, a previously undocumented Python RAT reserved exclusively for domain-joined hosts.
https://www.huntress.com/blog/malicious-browser-extention-crashfix-kongtuke
Malware Peddlers Are Now Hijacking Snap Publisher Domains
Alan Pope reports on a campaign which against highlights the risk posed by infrastructure which expires and can then be obtained by threat actors. To which we arguably have no good at scale solution..
There’s a relentless campaign by scammers to publish malware in the Canonical Snap Store. Some gets caught by automated filters, but plenty slips through. Recently, these miscreants have changed tactics - they’re now registering expired domains belonging to legitimate snap publishers, taking over their accounts, and pushing malicious updates to previously trustworthy applications. This is a significant escalation.
https://blog.popey.com/2026/01/malware-purveyors-taking-over-published-snap-email-domains/
Planned failure: Gootloader’s malformed ZIP actually works perfectly
Aaron Walton shows a trick employed to break detection but work when leveraged by the user. Another example of challenges where behaviours in parsing files are inconsistent. Note the detection opportunity..
Gootloader malware is delivered to victims in a ZIP archive and the ZIP itself is designed to bypass detection.
The ZIP archive is deliberately malformed causing many unarching tools to fail in analyzing it.
However, defenders can take advantage of its unique format and behaviors to build detections.
https://expel.com/blog/gootloaders-malformed-zip/
Organized Traffer Gang on the Rise Targeting Web3 Employees and Crypto Holders
Vlad Pasca and Radu-Emanuel Chiscariu detail an apparently financially motivated campaign which appears to have yielded some return. Scale of infrastructure, overlap in groups and more all noteworthy. Falls into at least the serious organised crime bucket..
Sophisticated cybercriminal operation targets cryptocurrency users and Web3 employees
Malware delivered through fake Electron applications disguised as legitimate tools
Uses extensive infrastructure of 80+ domains across multiple campaigns
Employs advanced social engineering with elaborate fake company ecosystems
Shared infrastructure suggests links to multiple traffer groups including “Marko Polo”, “CrazyEvil”, and “Wagmi”
Documented earnings of at least $2.4 million from cryptocurrency theft
https://hybrid-analysis.blogspot.com/2026/01/organized-traffer-gang-on-rise.html
How Two Leaks Unmasked the Criminal Network of Yalishanda aka Media Land, and BlackBasta
Analyst1 cross refence various sources to understand the interconnection between various ransomware eco-system elements.
The leaks of BlackBasta’s internal chats and Media Land gave us something rare: a clear look into how ransomware groups actually operate and who helps them do it. Together, the leaks gave investigators, analysts, and defenders an unprecedented opportunity to map the evolution of modern cybercriminal infrastructure into a professionalized, scalable, and compartmentalized system. Names became faces. And yet, the story isn’t over.
Even after being named or sanctioned, many of the people involved, such as Volosovik and Zatolokin, remain active. Their infrastructure is built to survive. They rotate domains, change wallets, and use new Telegram handles. They adapt. That’s what makes fighting this ecosystem so hard.
https://analyst1.com/infrastructure-in-the-shadows/
Inside a Malicious Push Network: What 57M Logs Taught Us
Infoblox register expired infrastructure for good intent and gains insight into the scale of campaign.
Who doesn’t love to eavesdrop onto a juicy conversation? We recently snooped on the communications of an affiliate advertising push notification system whose DNS records were left misconfigured–oops. This mistake allowed us to receive a copy of every ad they sent victims, along with all the metrics they recorded. We analyzed over 57M logs collected over a two-week period that contained advertisements, requests for software upgrades, and other events.
As interesting as the data was, the method we employed was even more fun. We used a DNS technique to take control of a domain abandoned by the threat actor by simply claiming it at the DNS provider. For the DNS geeks out there: we took advantage of a lame name server delegation.
But why listen to just one conversation when you can listen to many? It turns out this actor demonstrated poor DNS hygiene, including multiple misconfigured delegations. Within a day, we’d increased our collection from one domain to nearly 120. Thousands of victim devices were connecting to our server and creating 30MB per second of logs.
Attack on *stan: Your malware, my C2
Ctrl-Alt-Int3l also registers a domain for good intent..
While hunting for C2 infrastructure on Censys, we uncovered a suspected state-affiliated cluster targeting Kazakh and Afghan entities in a persistent campaign, with C2 servers active at the time of writing (20th Jan 2026) that have been operating unreported since at least August 2022.
Due to an operational mistake by the adversary, we now own one of their KazakRAT C2 domains, allowing us to redirect victim traffic to a sinkhole to passively collect victim IP addresses beaconing home.
https://ctrlaltintel.com/threat%20research/KazakRAT/
Discovery
How we find and understand the latent compromises within our environments.
Mega RMM KQL Query
Daniel Card releases this is extraordinary KQL query to detect Remote Management & Monitoring solutions..
https://github.com/mr-r3b00t/rmm_from_shotgunners_rmm_lol/blob/main/mega_rmm_query.kql
Defence
How we proactively defend our environments.
Pre-Draft Call for Comments: Guide to Operational Technology (OT) Security
NIST issues this call for comments on OT security.
NIST has initiated the process of revising SP 800-82, Guide to Operational Technology (OT) Security, to incorporate lessons learned, align with relevant NIST guidance (e.g., Cybersecurity Framework (CSF) 2.0, NIST IR 8286 Rev. 1, NIST SP 800-53 Rev. 5.2.0) and OT cybersecurity standards and practices, and address changes in the OT threat landscape.
NIST invites the public to suggest improvements on the document’s effectiveness, relevance, and general use to better help the OT community understand and manage their cybersecurity risk.
The public comment period is open through February 23, 2026.
https://csrc.nist.gov/pubs/sp/800/82/r4/iprd
After the Takedown: Excavating Abuse Infrastructure with DNS Sinkholes
Max van der Horst shows the value of DNS sinkholes (as various bits of reporting above support)..
DNS sinkholing is usually treated as the end point of an abuse campaign: a moment when malicious domains are neutralized and infrastructure disappears from view. This post argues that sinkholing instead creates an analytical boundary. While it disrupts ongoing harm, it also freezes DNS configuration at the moment of intervention, preserving a structured record of how abuse infrastructure was organized beforehand. Using passive DNS alone, I examine sinkholing activity at scale and show that takedowns occur in concentrated bursts rather than as continuous clean-up. A detailed analysis of the April 2025 Badbox 2.0 takedown demonstrates how pre-takedown hosting choices, nameserver reuse, and large-scale programmatic subdomain generation remain visible after intervention. Treated this way, sinkholes are not just defensive tools, but post-action artifacts that make abuse infrastructure briefly legible.
https://disclosing.observer/2026/01/14/excavating-abuse-infrastructure-dns-sinkholes.html
ConsentFix: Securing Your Tenant Against OAuth Authorisation Code Theft
Toby G outlines a defence strategy for this challenge..
The solution revolves around a fundamental principle in Entra ID: requiring user assignment. When you set
AppRoleAssignmentRequiredtotrueon a service principal, only explicitly assigned users can authenticate to that application. This breaks the ConsentFix attack at the first step—random users can no longer consent to these applications, even though they’re Microsoft first-party apps.The clever part is creating these service principals proactively. Normally, a service principal only exists after someone in your tenant has used the application. By creating them before any attacker-initiated OAuth flow, we maintain control over who can authenticate.
https://sentinel.blog/consentfix-securing-your-tenant-against-oauth-authorisation-code-theft/
Creating a Rust VBS Enclave DLL running in VTL1
flux shows how to pragmatically use VBS enclaves in Rust.
We will build an application where the secure VTL1 DLL has a secret password in memory, and the normal application will pass passwords to it. The normal application has no idea what is in the secure memory, so we can only find whether we had a valid password or not after calling the secure function!
https://fluxsec.red/creating-a-rust-application-running-in-vtl1
6-day and IP Address Certificates are Generally Available
Matthew McPherrin announces and outlines the rational for short lived TLS certificates for IP addresses. Obviously misuse is going to be a real risk here on reused infrastructure..
IP address certificates allow server operators to authenticate TLS connections to IP addresses rather than domain names. Let’s Encrypt supports both IPv4 and IPv6. IP address certificates must be short-lived certificates, a decision we made because IP addresses are more transient than domain names, so validating more frequently is important.
https://letsencrypt.org/2026/01/15/6day-and-ip-general-availability
NOVA Claude Code Protector
Thomas Roccia releases this demonstration on how we might protect these class of systems in an AI world..
Features
Session Tracking - Captures all tool usage with timestamps and metadata
Prompt Injection Detection - Three-tier scanning (keywords, semantic ML, LLM) - passive monitoring with warnings
Dangerous Command Blocking - Actively prevents destructive operations before execution
MCP & Skills Tracing - Tracks MCP server calls and Agent Skills invocations with detailed breakdowns
Interactive HTML Reports - Visual timeline, conversation trace, and expandable event details
AI-Powered Summaries - Intelligent session summaries via Claude Haiku
Configurable - Custom report locations, detection thresholds, and rules
https://github.com/fr0gger/nova-claude-code-protector
Incident Writeups & Disclosures
How they got in and what they did.
Vulnerability
Our attack surface.
StackWarp: Breaking AMD SEV-SNP Integrity via Deterministic Stack-Pointer Manipulation through the CPU’s Stack Engine
Ruiyi Zhang, Tristan Hornetz, Daniel Weber, Fabian Thomas and Michael Schwarz do some world class vulnerability research (and reverse engineering) which continue to highlight the the work to be done on compute foundations.
In this paper, we present StackWarp, a software-based architectural attack exploiting the stack engine on AMD Zen CPUs to modify the stack pointer within an SEV-SNP guest, fully breaking integrity. StackWarp relies on an undocumented bit within a shared model-specific register (MSR) available on AMD Zen 1–5 CPUs that enables or disables the stack engine. Our reverse engineering shows that the state of the stack engine is not correctly synchronized across the logical cores, allowing an attacker to deterministically adjust the stack pointer on the sibling logical core across Zen generations, including fully patched Zen 5. We discover StackWarp via a systematic exploration of the MSR space, including undocumented MSRs. By flipping MSR bits, we discover bits that affect SEV-SNP guests running on a sibling logical core. To demonstrate the security impact, we show StackWarp in four end-to-end attacks on SEV-SNP guests: RSA-CRT privatekey recovery, OpenSSH password-authentication bypass, and privilege escalations using either sudo or a kernel-mode ROP chain.
https://cispa.de/news/2026/stackwarp-final.pdf
CVE-2026-0227 PAN-OS: Firewall Denial of Service (DoS) in GlobalProtect Gateway and Portal
Palo Alto Networks warns..
A vulnerability in Palo Alto Networks PAN-OS software enables an unauthenticated attacker to cause a denial of service (DoS) to the firewall. Repeated attempts to trigger this issue results in the firewall entering into maintenance mode.
https://security.paloaltonetworks.com/CVE-2026-0227
CVE-2026-20965: Cymulate Research Labs Discovers Token Validation Flaw that Leads to Tenant-Wide RCE in Azure Windows Admin Center
Ilan Kalendarov, Ben Zamir and Elad Beber details a vulnerability which will need some patching..
Cymulate first reported the issue to Microsoft in August 2025. CVE-2026-20965 exposes how subtle failures in token validation and access scoping can undermine cloud isolation guarantees. To provide a fix for the issue, Microsoft released Windows Admin Center Azure Extension version 0.70.00 January 13, 2026. Cymulate encourages all cloud deployments of Windows Admin Center Azure to apply the update as soon as possible.
On the same day as the Microsoft disclosure, Cymulate Exposure Validation was updated with attack scenario Azure - Scan For Azure WindowsAdminCenter Improper Token Validation Vulnerability CVE-2026-20965 to test this vulnerability in your environment.
https://cymulate.com/blog/cve-2026-20965-azure-windows-admin-center-tenant-wide-rce/
Suricata 8.0.3 and 7.0.14 address vulnerabilities
Various critical and high vulnerabilities which at best could cause denial of service and potentially far worse..
https://suricata.io/2026/01/13/suricata-8-0-3-and-7-0-14-released/
GNU InetUtils Security Advisory: remote authentication by-pass in telnetd
Simon Josefsson discloses a vulnerability which as ‘90s vibes..
The telnetd server invokes /usr/bin/login (normally running as root) passing the value of the USER environment variable received from the client as the last parameter.
If the client supply a carefully crafted USER environment value being the string “-f root”, and passes the telnet(1) -a or --login parameter to send this USER environment to the server, the client will be automatically logged in as root bypassing normal authentication processes.
https://seclists.org/oss-sec/2026/q1/89
Offense
Attack capability, techniques and trade-craft.
Tangled
Released last month, but I missed this release by Inés Martín which defensive teams will want to ensure detection coverage for due to the inability to likely block calendar invites.
Tangled is a phishing platform designed from an offensive security perspective.
It automates many of the aspects of social engineering campaigns delivery and weaponizes iCalendar rendering features in Microsoft Outlook & Gmail (Google Workspace) to deliver spoofed meeting invites that are automatically added to a user's calendar without interaction.
https://github.com/ineesdv/Tangled
Sliver tor bridge
Otsmane Ahmed releases this capability which is going to complicate attribution further.
Tor-based transport bridge for Sliver c2. creates a hidden service and proxies traffic to your sliver server so your real IP is never exposed.
https://github.com/Otsmane-Ahmed/sliver-tor-bridge
GhostWrite
Maldevel releases some anti-forensic capability..
These scripts help you edit files while maintaining their original "Modified" date in file managers (Windows Explorer, Finder on macOS, file browsers on Linux). This is useful when you need to preserve the appearance of when a file was last modified, even after editing
https://github.com/Logisek/GhostWrite
Self Decrypting Binary Generator
Claes M Nyberg wrote this in 2006 but the utility to offensive tooling protection is worth noting.
The SDC program creates self decrypting binaries for common operating systems and architectures. The target file is encrypted using Blowfish in Ciphertext Feedback Mode (CFB) and appended to an executable which reads itself and attempts to decrypt the appended data when it is run.
https://github.com/claesmnyberg/sdc
AV/EDR Killer
M0kht4r releases this capability and hopefully coverage will accelerate inclusion to the block list..
wsftprm.sys, signed by TPZ SOLUCOES DIGITAIS LTDA, and previously exposed to a local privilege escalation vulnerabliy publicly disclosed asCVE-2023-52271, but somehow still NOT on Microsoft's driver blocklist!!
https://github.com/xM0kht4r/AV-EDR-Killer
Exploitation
What is being exploited..
Attackers With Decompilers Strike Again (SmarterTools SmarterMail WT-2026-0001 Auth Bypass)
Piotr Bazydlo tells a story of patch bypasses and in the wild exploitation..
This issue was patched in version 9511, released on January 15, 2026. If you have not already upgraded, do so immediately.
Tooling and Techniques
Low level tooling and techniques for attack and defence researchers
Global Struct Dissector
Willi Ballenthin releases this work aid for something I always found deeply unintuitive..
Global Struct Dissector is an IDA Pro plugin that renders data in the disassembly view in a clear, readable format with explicit field names, offsets, and values. The plugin hooks IDA's data rendering system to intercept structure instances in global data segments and formats them using indentation, color syntax highlighting, and organized field listings.
https://github.com/williballenthin/idawilli/tree/master/plugins/global_struct_dissector
IDA Plugin IID to String
YungBinary releases this work aid for those working with COM on Windows.
A plugin for IDA that converts IID/GUID data structures to string and adds comments where the IID is referenced
https://github.com/YungBinary/IDA_Plugin_IID_to_String
Footnotes
Some other small (and not so small) bits and bobs which might be of interest.
Annual, quarterly and monthly reports
Nothing overly of note this week, but keep an eye on the Awesome Annual Security Reports 2026 collection
Artificial intelligence
Fundamental
Nothing overly of note this week
Applied non-cyber
Applied cyber specific
Agent Skills in the Wild: An Empirical Study of Security Vulnerabilities at Scale
CaMeLs Can Use Computers Too: System-level Security for Computer Use Agents
AgentGuardian: Learning Access Control Policies to Govern AI Agent Behavior
The Promptware Kill Chain: How Prompt Injections Gradually Evolved Into a Multi-Step Malware
AgenticRed: Optimizing Agentic Systems for Automated Red-teaming
An Empirical Study on Remote Code Execution in Machine Learning Model Hosting Ecosystems
LLM Security and Safety: Insights from Homotopy-Inspired Prompt Obfuscation
Husn Canaries: Defense-In-Depth for AI Coding Assistant Governance
Vulnerabilities i.e. insufficient secure development lifecycle
Books
Nothing overly of note this week
Events
CHERI Blossoms Conference 2026 - March 26th - 27th, 2026
Finally finally the NCSC’s podcast series.
Unless stated otherwise, linked or referenced content does not necessarily represent the views of the NCSC and reference to third parties or content on their websites should not be taken as endorsement of any kind by the NCSC. The NCSC has no control over the content of third party websites and consequently accepts no responsibility for your use of them.
This newsletter is subject to the NCSC website terms and conditions which can be found at https://www.ncsc.gov.uk/section/about-this-website/terms-and-conditions and you can find out more about how will treat your personal information in our privacy notice at https://www.ncsc.gov.uk/section/about-this-website/privacy-statement.